Skyrelis Behavioral Analytics for Agentic AI Systems
Proactively securing autonomous workflows across organizations
Agentic AI is transforming how organizations operate—autonomous agents now make decisions, execute tasks, and interact across systems at machine speed. But this evolution introduces a new security frontier. Protection must extend beyond human users to the agents themselves.
At Skyrelis, we're developing a behavioral analytics platform purpose-built for the Agentic AI era. Unlike legacy security tools focused solely on human actions or static rules, our engine is designed to dynamically monitor AI-driven workflows, detect risk in real-time, and provide organizations the visibility they need to stay ahead of threats—at the speed of automation.
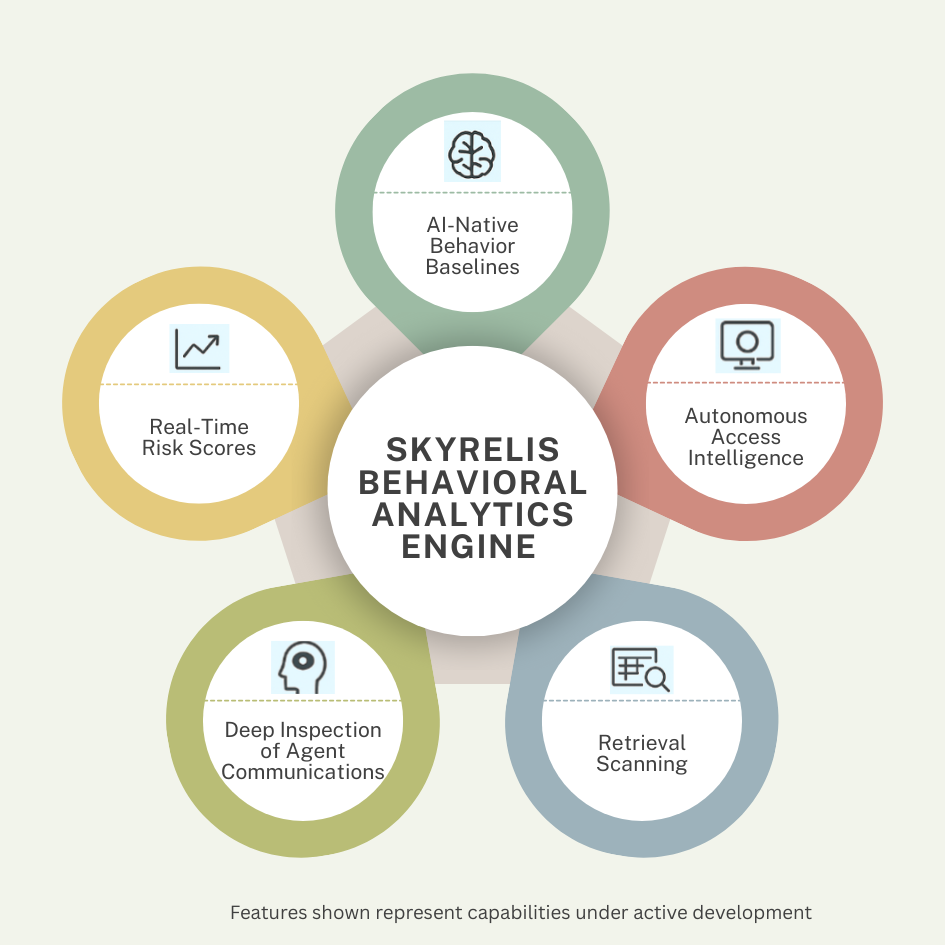
Features shown represent capabilities under active development
What Makes Skyrelis Different
1. AI-Native Behavior Baselines
Our platform is designed to learn the normal behavior of AI agents across your environment—spanning APIs, tools, data lakes, and custom workflows.
By establishing behavioral baselines, we aim to detect anomalies instantly—whether it's an agent querying unauthorized documents, chaining APIs in unexpected ways, or escalating privileges without precedent.
2. Deep Inspection of Agent Communications
We will scan inter-agent conversations in real-time to surface embedded secrets, tokens, or misconfigurations. Even mid-task credential leaks—hidden inside chained instructions or nested API calls—will be flagged in real time.
3. Autonomous Access Intelligence
We're building the capability to continuously map agent behavior: which identities they assume, which tools they invoke, and how data flows between systems.
This provides fine-grained visibility into LLM-initiated activity that is the first step before setting up guardrails to ensure agents only access the systems and data they're authorized to interact with.
4. RAG Input & Output Filtering
RAG (Retrieval-Augmented Generation) systems introduce risks from both queries and the retrieved content. We are aiming to address both ends:
Pre-Retrieval (Input) Scanning
Detect prompt injection attempts, sanitize ambiguous or risky queries, and validate origin (user, system, or agent) before reaching the retriever.
Post-Retrieval Filtering
Automatically screen retrieved documents for sensitive terms, stale or untrusted content, and apply metadata-based access controls (e.g., freshness, confidence, classification).
Output Monitoring
Ensure LLM outputs adhere to security policy—preventing the leakage of proprietary data, hallucinated responses, or regulatory violations.
5. Multi-Agent Risk Correlation
We're building the ability to track agent interactions across applications, clouds, and organizational domains. The goal is to identify emerging risks—such as recursive prompting loops or lateral movement —before they escalate.
6. Real-Time Threat Scoring
Every agent action will be assigned a contextual risk score with actionable recommendations—based on behavioral history, intent, and deviations from baseline.
Security teams will be alerted or use their existing security tools to trigger automated responses, enabling proactive intervention before damage occurs.
Join Our Innovation Circle
Skyrelis invites small to medium-sized high-tech companies ready to scale their AI solutions to join our Innovation Circle. Our goal is not to boil the ocean, but to deliver simple, focused, and effective data and API-centric security solutions tailored specifically for your growth and scalability needs. Your feedback will directly influence product development, ensuring the solutions we build closely match your business requirements. Join us to shape the future of simplified, targeted security solutions.
👉 Join our Innovation Circle todayDisclaimer: The above capabilities represent Skyrelis's product roadmap vision and are currently under development. Availability is subject to change based on direct customer feedbacks from our Innovation Circle and product development timelines.