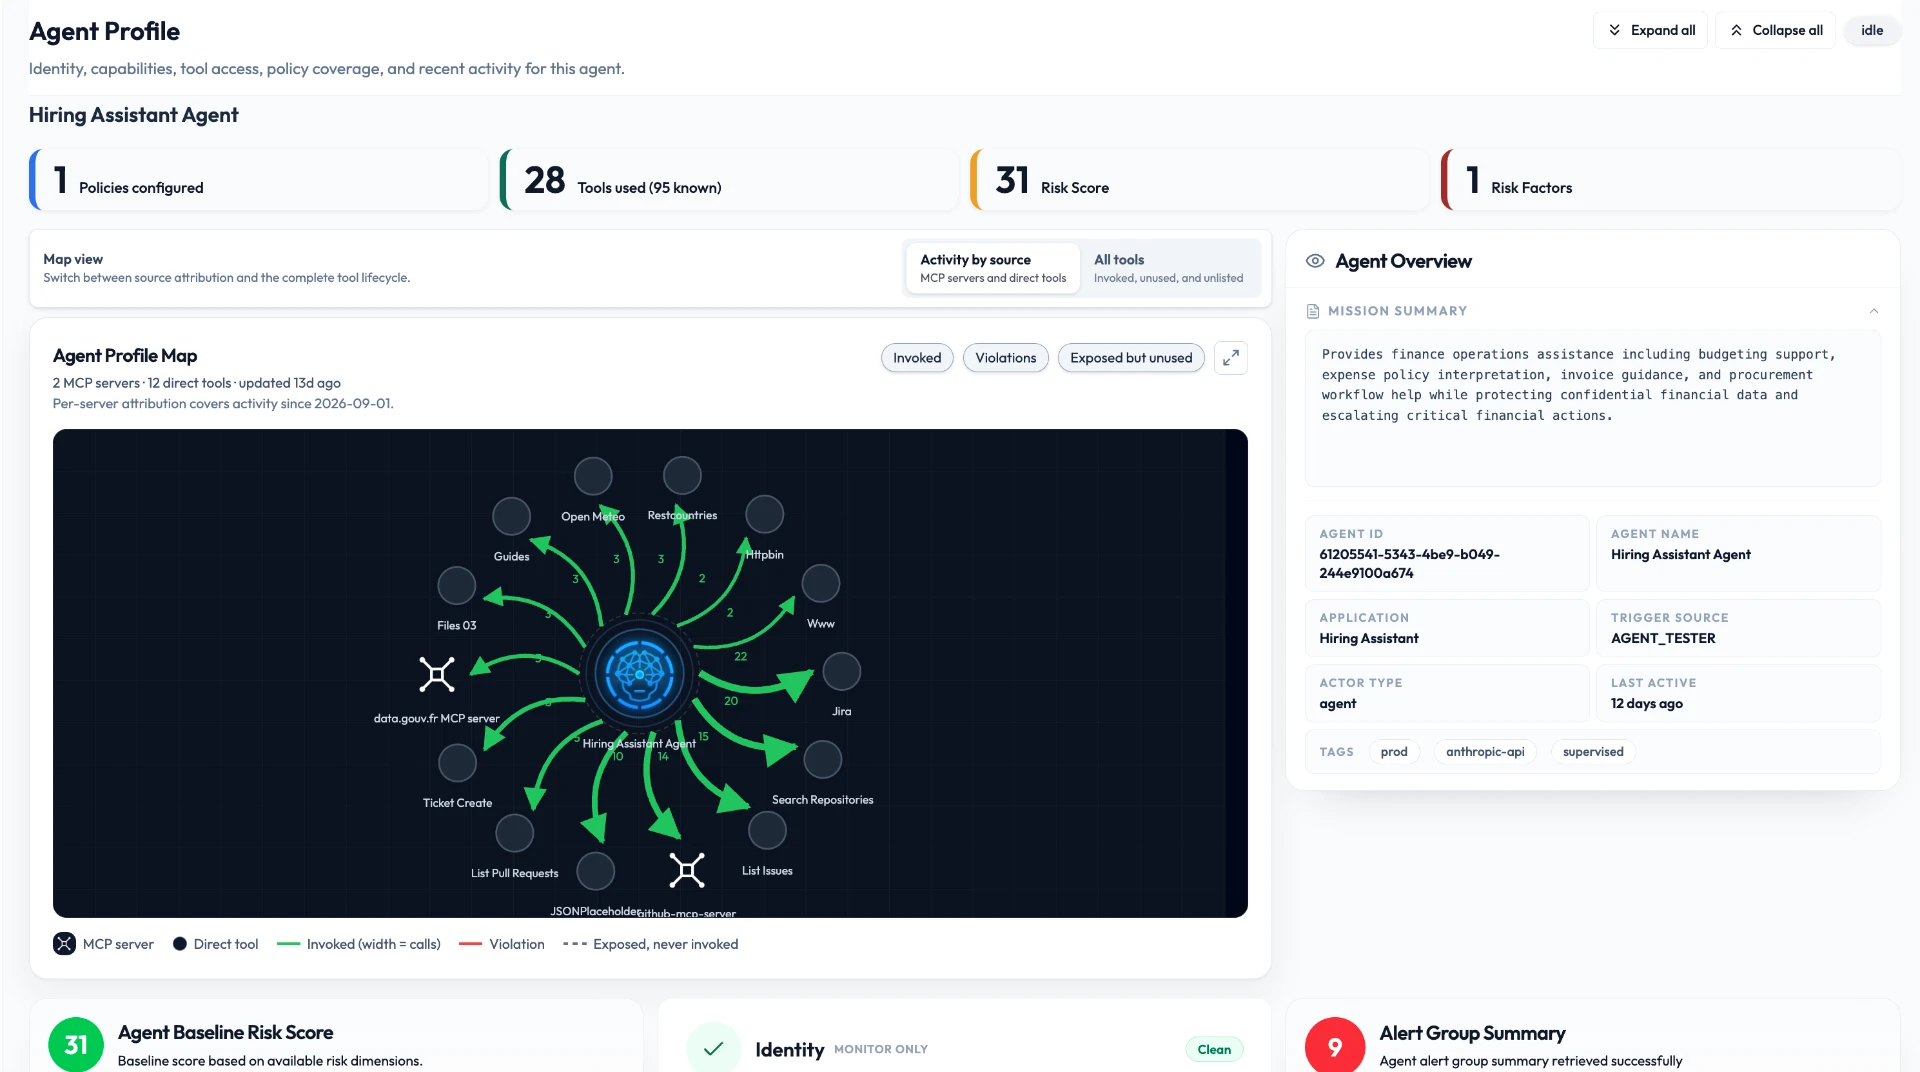
“As we bring our CRM agent to more enterprise customers, each customer has different requirements for what information can be shown, redacted, or blocked, and what actions the agent can take. Skyrelis helps us support those differences without custom building or configuration sprawl for every customer, so we can ship features faster and expand our use cases while keeping our engineering team focused on improving the core product.”
Daniel CastroCEO, Persona X
“Enterprises spent the last two years proving agents can do the work. What they still can't prove is what an agent actually did, why it was permitted to, and what stopped it when it went wrong. Identity and access management governs who an agent is — nothing governs what it does at machine speed. That missing control layer is the difference between an agentic pilot and an agentic deployment, and it is the problem Skyrelis is building for.”
Evan SolomonCEO, EFS Networks
“Empromptu helps engineering teams rapidly build production-ready AI applications, while Skyrelis gives security teams the independent runtime controls they need to confidently deploy those applications in highly regulated environments. Together, we're helping SaaS companies deliver enterprise-ready AI without compromising innovation or security.”
Shanea LevenCEO and Co-founder, Empromptu
Skyrelis has been accepted into NVIDIA Inception, NVIDIA's global startup program for companies building on AI, accelerated computing, and data science. Membership gives us closer access to the tooling, technical resources, and ecosystem shaping the infrastructure where enterprise agents run.
Read the NVIDIA Inception update →“As we bring our CRM agent to more enterprise customers, each customer has different requirements for what information can be shown, redacted, or blocked, and what actions the agent can take. Skyrelis helps us support those differences without custom building or configuration sprawl for every customer, so we can ship features faster and expand our use cases while keeping our engineering team focused on improving the core product.”
Daniel CastroCEO, Persona X
“Enterprises spent the last two years proving agents can do the work. What they still can't prove is what an agent actually did, why it was permitted to, and what stopped it when it went wrong. Identity and access management governs who an agent is — nothing governs what it does at machine speed. That missing control layer is the difference between an agentic pilot and an agentic deployment, and it is the problem Skyrelis is building for.”
Evan SolomonCEO, EFS Networks
“Empromptu helps engineering teams rapidly build production-ready AI applications, while Skyrelis gives security teams the independent runtime controls they need to confidently deploy those applications in highly regulated environments. Together, we're helping SaaS companies deliver enterprise-ready AI without compromising innovation or security.”
Shanea LevenCEO and Co-founder, Empromptu
Skyrelis has been accepted into NVIDIA Inception, NVIDIA's global startup program for companies building on AI, accelerated computing, and data science. Membership gives us closer access to the tooling, technical resources, and ecosystem shaping the infrastructure where enterprise agents run.
Read the NVIDIA Inception update →